

This example shows how to set up one-way Web access using a TCP flag in an ACL. PC 1 can access FTP server 1 and FTP server 2, but PC 2 can access only FTP server 2.
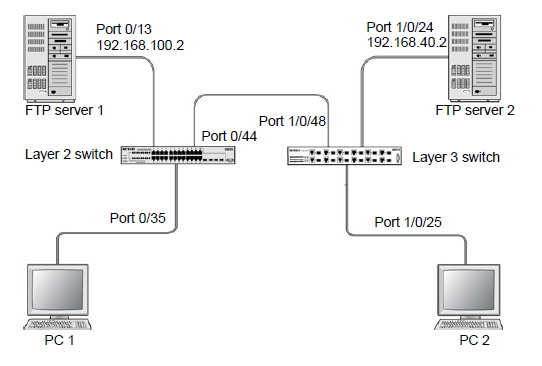
This is a two-part process:
- Configuring the Switch
- Configuring the GSM7342S Switch
Configuring the Switch
- Create VLAN 30 with IP address 192.168.30.1/24.
- Select Routing > VLAN > VLAN Routing Wizard.
A screen similar to the following displays.n the VLAN Routing Wizard.
- In the VLAN Routing Wizard, enter the following information:
- In the Vlan ID field, enter 30.
- In the IP Address field, enter 192.168.30.1.
- In the Network Mask field, enter 255.255.255.0.
- Click Unit 1. The ports display.
- Click the gray box under port 35 twice until U displays.
The U specifies that the egress packet is untagged for the port.
- Click Apply to save VLAN 30.
- Select Routing > VLAN > VLAN Routing Wizard.
- Create VLAN 100 with IP address 192.168.100.1/24.
- Select Routing > VLAN > VLAN Routing Wizard.
A screen similar to the following displays.
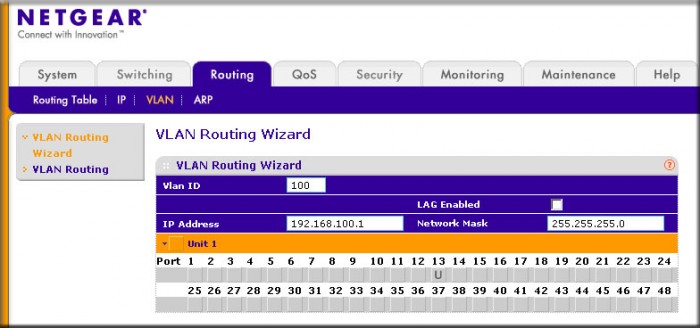
- Enter the following information:
- In the Vlan ID field, enter 100.
- In the IP Address field, enter 192.168.100.1.
- In the Network Mask field, enter 255.255.255.0.
- Click Unit 1. The ports display.
- Click the gray box under port 13 twice until U displays. The U specifies that the egress packet is untagged for the port.
- Click Apply to save VLAN 100.
- Select Routing > VLAN > VLAN Routing Wizard.
- Create VLAN 200 with IP address 192.168.200.1/24.
- Select Routing > VLAN > VLAN Routing Wizard.
A screen similar to the following displays.
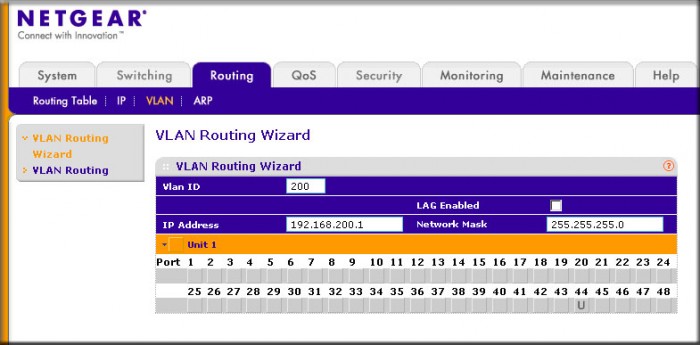
- Enter the following information:
- In the Vlan ID field, enter 200.
- In the IP Address field, enter 192.168.200.1.
- In the Network Mask field, enter 255.255.255.0.
- Click Unit 1. The ports display.
- Click the gray box under port 44 twice until U displays. The U specifies that the egress packet is untagged for the port.
- Click Apply to save VLAN 200.
- Select Routing > VLAN > VLAN Routing Wizard.
- Enable IP routing.
- Select Routing > IP > Basic > IP Configuration.
A screen similar to the following displays.
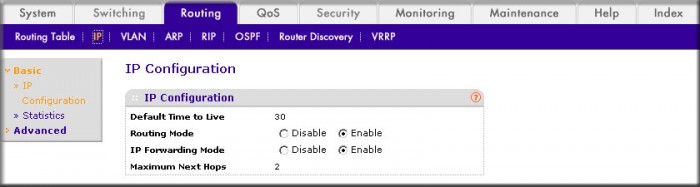
- Under IP Configuration, make the following selections:
- For Routing Mode, select the Enable radio button.
- For IP Forwarding Mode, select the Enable radio button.
- Click Apply to enable IP routing.
- Select Routing > IP > Basic > IP Configuration.
- Add a static route with IP address 192.268.40.0/24:
- Select Routing > Routing Table > Basic > Route Configuration.
A screen similar to the following displays.
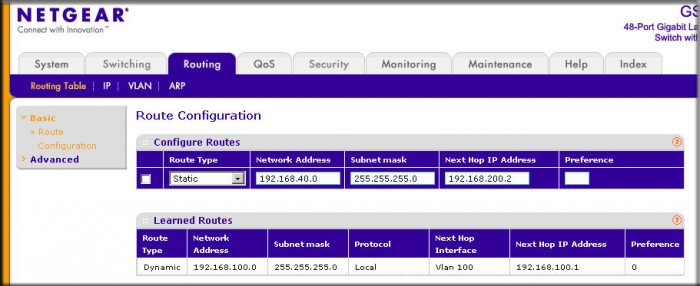
- Under Configure Routes, make the following selection and enter the following information:
- In the Route Type list, select Static.
- In the Network Address field, enter 192.168.40.0.
- In the Subnet Mask field, enter 255.255.255.0.
- In the Next Hop IP Address field, enter 192.168.200.2.
- Click Add.
- Select Routing > Routing Table > Basic > Route Configuration.
- Create a static route with IP address 192.168.50.0/24:
- Select Routing > Routing Table > Basic > Route Configuration.
A screen similar to the following displays.
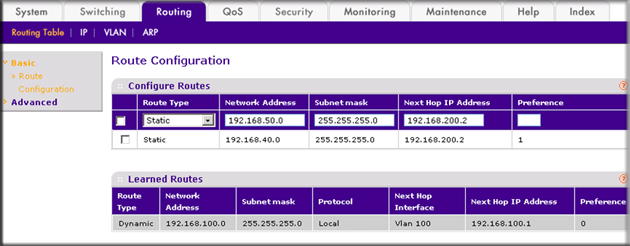
- Under Configure Routes, make the following selection and enter the following information:
- In the Route Type list, select Static.
- In the Network Address field, enter 192.168.50.0.
- In the Subnet Mask field, enter 255.255.255.0.
- In the Next Hop IP Address field, enter 192.168.200.2.
- Click Add.
- Select Routing > Routing Table > Basic > Route Configuration.
- Create an ACL with ID 101.
- Select Security > ACL > Advanced > IP ACL.
A screen similar to the following displays.
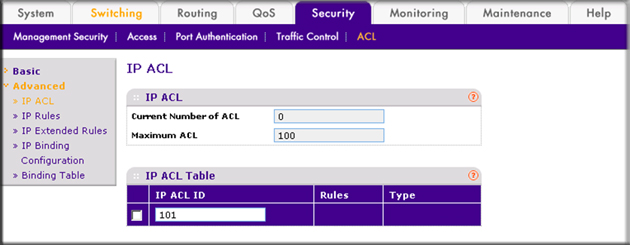
- In the IP ACL Table, in the IP ACL ID field, enter 101.
- Click Add.
- Select Security > ACL > Advanced > IP ACL.
- Create an ACL with ID 102.
- Select Security > ACL > Advanced > IP ACL.
A screen similar to the following displays.
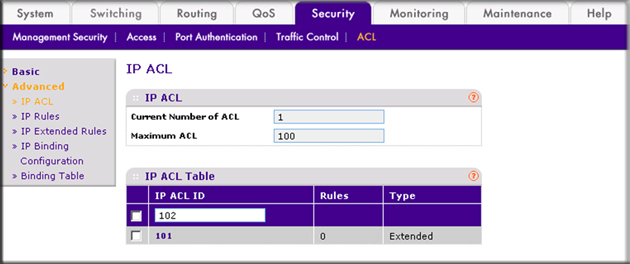
- In the IP ACL Table, in the IP ACL ID field, enter 102.
- Click Add.
- Select Security > ACL > Advanced > IP ACL.
- Add and configure an IP extended rule that is associated with ACL 101.
- Select Security > ACL > Advanced > IP Extended Rules.
A screen similar to the following displays.

- Under IP Extended Rules, in the ACL ID list, select 10.
- Click Add.
The Extended ACL Rule Configuration screen displays.
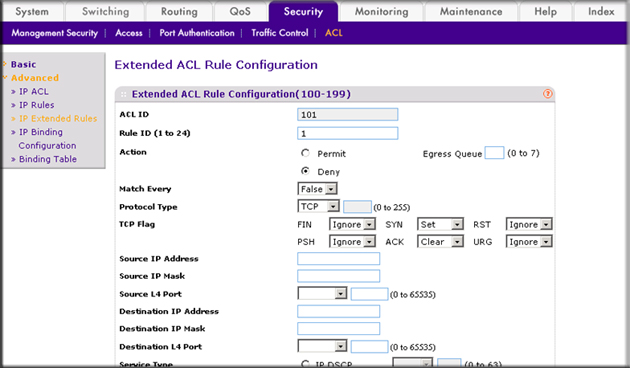
- Under Extended ACL Rule Configuration (100-199), enter the following information and make the following selections:
- In the Rule ID field, enter 1.
- For Action mode, select the Deny radio button.
- In the Match Every field, select False.
- In the Protocol Type list, select TCP.
- For TCP Flag, in the SYN field, select Set, and in the ACK field, select Clear.
- Click Apply to save the settings.
- Select Security > ACL > Advanced > IP Extended Rules.
- Add and configure an IP extended rule that is associated with ACL 102.
- Select Security > ACL > Advanced > IP Extended Rules.
A screen similar to the following displays.

- Under IP Extended Rules, in the ACL ID list, select 102.
- Click Add. The Extended ACL Rule Configuration screen displays.
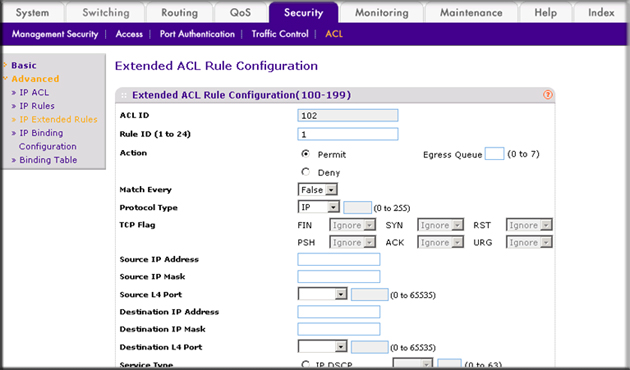
- Under Extended ACL Rule Configuration (100-199), enter the following information and make the following selections:
- In the Rule ID field, enter 1.
- For Action, select the Permit radio button.
- In the Match Every field, select False.
- In the Protocol Type list, select IP.
- Click Apply to save the settings.
- Select Security > ACL > Advanced > IP Extended Rules.
- Apply ACL 101 to port 44.
- Select Security > ACL > Advanced > IP Binding Configuration.
A screen similar to the following displays.
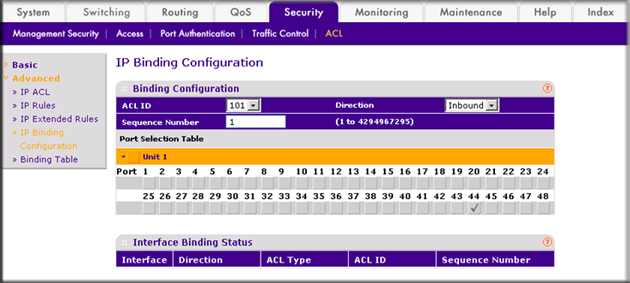
- Under Binding Configuration, specify the following:
- In the ACL ID list, select 101.
- In the Sequence Number field, enter 1.
- Click Unit 1. The ports display.
- Click the gray box under port 44.
A check mark displays in the box.
- Click Apply to save the settings.
- Select Security > ACL > Advanced > IP Binding Configuration.
- Apply ACL 102 to port 44.
- Select Security > ACL > Advanced > IP Binding Configuration.
A screen similar to the following displays.
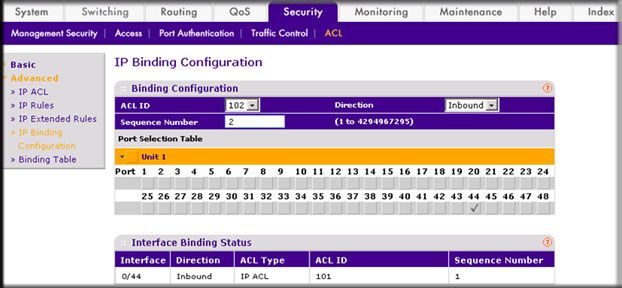
- Under Binding Configuration, make the following selection and enter the following information:
- In the ACL ID list, select 102.
- In the Sequence Number field, enter 2.
- Click Unit 1. The ports display.
- Click the gray box under port 44. A check mark displays in the box.
- Click Apply to save the settings.
- Select Security > ACL > Advanced > IP Binding Configuration.
Configuring the GSM7342S Switch
- Create VLAN 40 with IP address 192.168.40.1/24.
- Select Routing > VLAN > VLAN Routing Wizard.
A screen similar to the following displays.
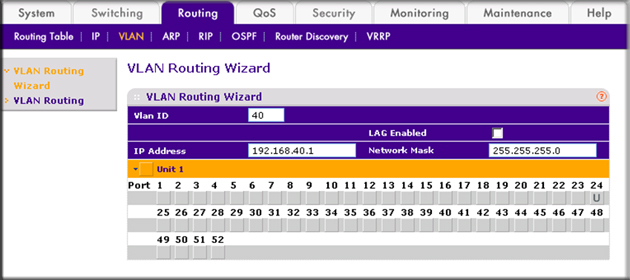
- Enter the following information:
- In the Vlan ID field, enter 40.
- In the IP Address field, enter 192.168.40.1.
- In the Network Mask field, enter 255.255.255.0.
- Click Unit 1. The ports display.
- Click the gray box under port 24 twice until U displays. The U specifies that the egress packet is untagged for the port.
- Click Apply to save VLAN 40.
- Select Routing > VLAN > VLAN Routing Wizard.
- Create VLAN 50 with IP address 192.168.50.1/24:
- Select Routing > VLAN > VLAN Routing Wizard.
A screen similar to the following displays.
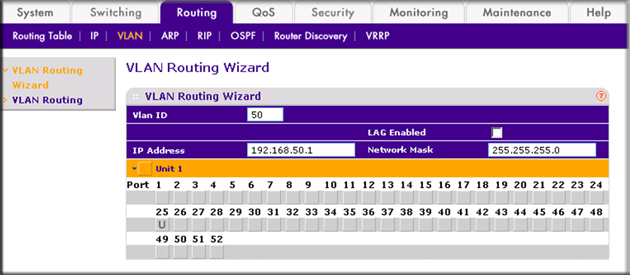
- Enter the following information:
- In the Vlan ID field, enter 50.
- In the IP Address field, enter 192.168.50.1.
- In the Network Mask field, enter 255.255.255.0.
- Click Unit 1. The ports display.
- Click the gray box under port 25 twice until U displays.
The U specifies that the egress packet is untagged for the port.
- Click Apply to save VLAN 50.
- Select Routing > VLAN > VLAN Routing Wizard.
- Create VLAN 200 with IP address 192.168.200.2/24.
- Select Routing > VLAN > VLAN Routing Wizard.
A screen similar to the following displays.
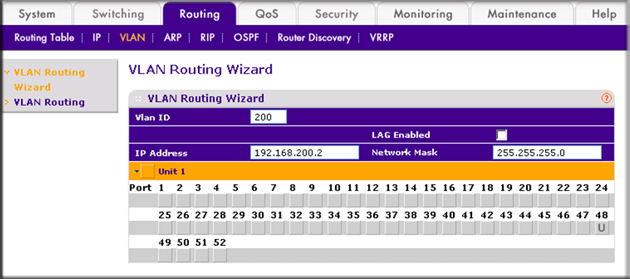
- Enter the following information:
- In the Vlan ID field, enter 200.
- In the IP Address field, enter 192.168.200.2.
- In the Network Mask field, enter 255.255.255.0.
- Click Unit 1.
The ports display.
- Click the gray box under port 48 twice until U displays.
The U specifies that the egress packet is untagged for the port.
- Click Apply to save VLAN 200.
- Select Routing > VLAN > VLAN Routing Wizard.
- Create a static route with IP address 192.168.100.0/24:
- Select Routing > Routing Table > Basic > Route Configuration.
A screen similar to the following displays.
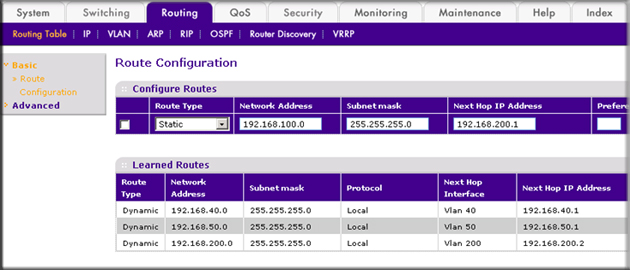
- Under Configure Routes, make the following selections and enter the following information:
- Select Static in the Route Type field.
- In the Network Address field, enter 192.168.100.0.
- In the Subnet Mask field, enter 255.255.255.0.
- In the Next Hop IP Address field, enter 192.168.200.1.
- Click Add.
- Select Routing > Routing Table > Basic > Route Configuration.
- Create a static route with IP address 192.168.30.0/24:
- Select Routing > Routing Table > Basic > Route Configuration.
A screen similar to the following displays.
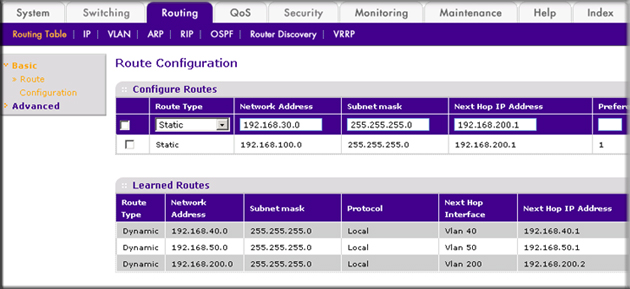
- Under Configure Routes, make the following selection and enter the following information:
- In the Route Type field, select Static.
- In the Network Address field, enter 192.168.30.0.
- In the Subnet Mask field, enter 255.255.255.0.
- In the Next Hop IP Address field, enter 192.168.200.1.
- Click Add.
- Select Routing > Routing Table > Basic > Route Configuration.
For more information, see the following support articles:
- What are Access Control Lists (ACLs) and how do they work with my managed switch?
- How do I use CLI commands on my managed switch to configure one-way access using a TCP flag in an Access Control List (ACL)?
This article applies to the following managed switches and their respective firmware:
- M5300 - firmware version 10.0.0.x
-
- M5300-28G (GSM7228S)
- M5300-5G (GSM7252S)
- M5300-28G3 (GSM7328Sv2h2)
- M5300-52G3 (GSM7352Sv2h2)
- M5300-28G_POE+ (GSM7228PSv1h2)
- M5300-52G-POE+ (GSM7252PSv1h2)
- M5300-28GF3 (GSM7328FSv2)
- M4100 - firmware version 10.0.1.x
-
- M4100-26G (GSM7224v2h2)
- M4100-50G (GSM7248v2h2)
- M4100-26G-POE (GSM7226Pv1h1)
- M4100-50G-POE+ (GSM7248Pv1h1)
- M4100-26G-POE (FSM7226Pv1h1)
- M4100-50-POE (FSM7250Pv1h1)
- M4100-D12G (GSM5212v1h1)
- M4100-D10-POE (FSM5210Pv1h1)
- M7100 - firmware version 10.0.1.x
-
- M7100-24X (XSM7224)
- XSM7224S - firmware version 9.0.1.x
Last Updated:07/07/2025
|
Article ID: 21717