

NETGEAR's Product Security Team has assessed the following product vulnerabilities and provided guidance to address these vulnerabilities in the table below.
Because firmware updates contain security fixes, bug fixes, and new features for your products, we strongly advise you to enable automatic firmware updates on supported devices. For older products, we advise you to download and install new firmware updates as soon as possible or follow the guidance provided for devices that require other remediation steps.
CVE-2026-109618, CVE-2026-109619 PHP2Shell remote code execution vulnerabilities
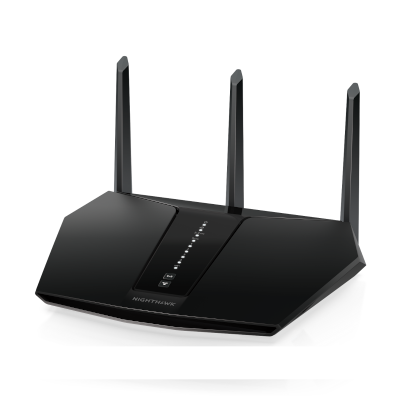
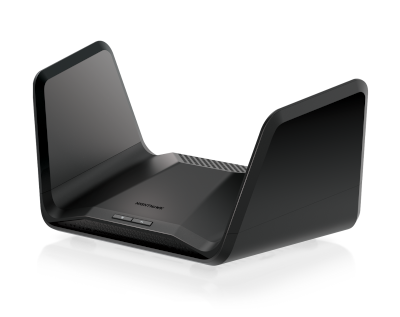
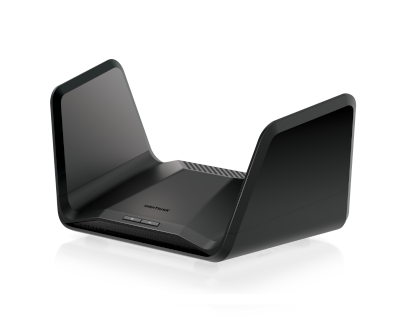
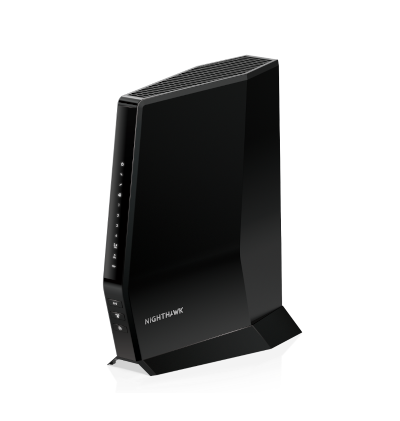
NETGEAR assessed PHP vulnerabilities CVE-2026-109618 (also known as PHP2Shell) and CVE-2026-109619. Only the Nighthawk models listed below were found to include PHP components and their actual impact is under review.
In these products, PHP is used only for local web management and accessible to users who have already connected to the WiFi network or LAN. It is not accessible from the Internet by default and cannot be exploited by remote attackers. NETGEAR has not seen any evidence of exploits targeting these devices.
No other NETGEAR product or service is exposed to these vulnerabilities based on our assessment.
Severity: MEDIUM
Recommendation
This advisory will be updated when fixed firmware versions are available for the affected products.
As a precaution and a best practice do not allow untrusted users to connect to your WiFi network.
Disclaimer: This document is provided on an "as is" basis and does not imply any kind of guarantee or warranty, including the warranties of merchantability or fitness for a particular use. Your use of the information in the document or materials linked to the document is at your own risk. NETGEAR reserves the right to change or update this document at any time. NETGEAR expects to update this document as new information becomes available.
The above-listed vulnerabilities remain if you do not complete all recommended steps. NETGEAR is not responsible for any consequences that could have been avoided by following the recommendations in this notification.