
NETGEAR's Product Security Team has assessed the following product vulnerabilities and provided guidance to address these vulnerabilities in the table below.
Because firmware updates contain security fixes, bug fixes, and new features for your products, we strongly advise you to enable automatic firmware updates on supported devices. For older products, we advise you to download and install new firmware updates as soon as possible or follow the guidance provided for devices that require other remediation steps.
CVE-2026-9215 CSRF vulnerability in some NETGEAR XR series gaming routers
A cross site request forgery (CSRF) vulnerability in the listed NETGEAR models allows an attacker, who can leverage social engineering techniques on a router administrator, to tamper with router configuration and disrupt router operations with active assistance from the router administrator. There is no confidentiality impact due to this vulnerability.
Severity: LOW
Acknowledgments: mornaner
Recommendation
Devices with automatic updates enabled may already have this patch applied. If not, please check the firmware version and update it to the latest. Fixed in:
| Product | Fixed Version |
|---|---|
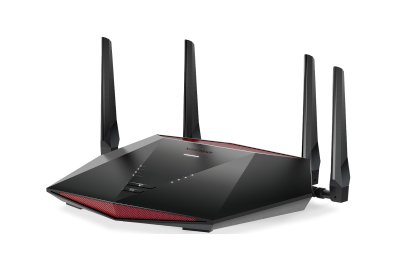
| XR1000v2 Nighthawk WiFi 6 Pro Gaming Router | V1.1.0.22 |
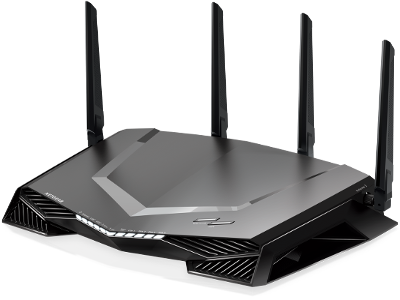
| XR500 (EoS) Nighthawk Pro Gaming Router | V2.3.5.152 |
Models marked (EoS) have reached End-of-Support phase, and no security updates are planned. NETGEAR strongly recommends that you retire these devices and upgrade to a newer NETGEAR device for continued security support.
CVE-2026-9216 Insufficient input validation vulnerability in some NETGEAR RAX series routers
The vulnerability allows a network-adjacent attacker with network access (such as WiFi credentials) to crash affected router's management UI. There is no confidentiality or integrity impact. A crash of the router's management UI does not impact the availability of the router's core services like its WiFi network.
Severity: LOW
Acknowledgments: mr_mee

Recommendation
Devices with automatic updates enabled may already have this patch applied. If not, please check the firmware version and update it to the latest. Fixed in:
| Product | Fixed Version |
|---|---|
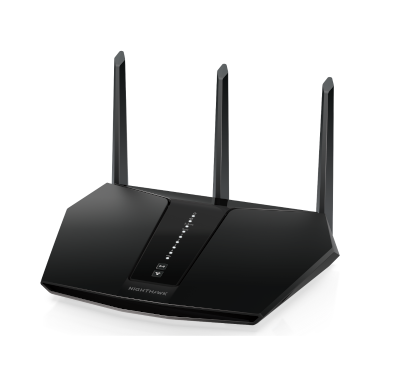
| RAX30 Nighthawk AX5 5-Stream AX2400 WiFi 6 Router | V1.0.9.92 |
| RAX35 Nighthawk AX4 4-Stream WiFi 6 Router | V1.0.10.72 |
| RAX38 (EoS) Nighthawk AX4 4-Stream AX3000 WiFi Router | V1.0.6.106 |
| RAX40 (EoS) Nighthawk AX4 4-Stream WiFi Router | V1.0.6.106 |
| RAXE300 Nighthawk AXE7800 Tri-Band WiFi 6E Router | V1.0.9.82 |
Models marked (EoS) have reached End-of-Support phase, and no security updates are planned. NETGEAR strongly recommends that you retire these devices and upgrade to a newer NETGEAR device for continued security support.
Disclaimer: This document is provided on an "as is" basis and does not imply any kind of guarantee or warranty, including the warranties of merchantability or fitness for a particular use. Your use of the information in the document or materials linked to the document is at your own risk. NETGEAR reserves the right to change or update this document at any time. NETGEAR expects to update this document as new information becomes available.
The above-listed vulnerabilities remain if you do not complete all recommended steps. NETGEAR is not responsible for any consequences that could have been avoided by following the recommendations in this notification
Revision History:
- Removed the XR1000 from CVE-2026-9215
- Corrected the FW fixed version for the RAXE300 in CVE-2026-9216