

NETGEAR's Product Security Team has assessed the following product vulnerabilities and provided guidance to address these vulnerabilities in the table below.
Because firmware updates contain security fixes, bug fixes, and new features for your products, we strongly advise you to enable automatic firmware updates on supported devices. For older products, we advise you to download and install new firmware updates as soon as possible or follow the guidance provided for devices that require other remediation steps.
Affected Products
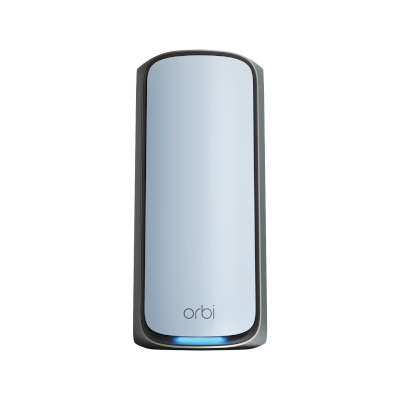
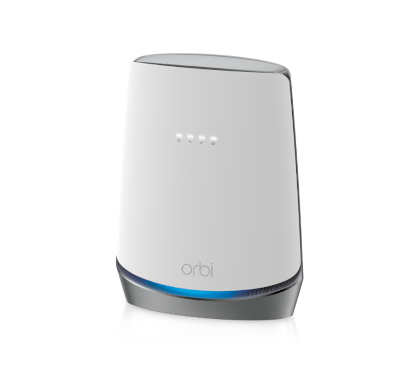
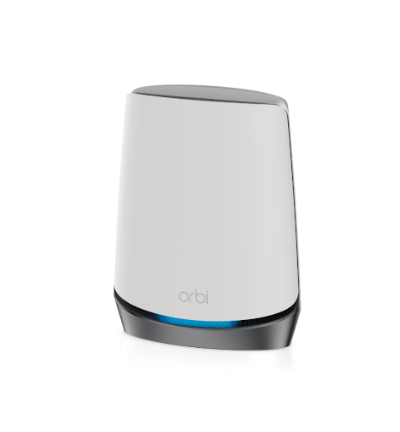


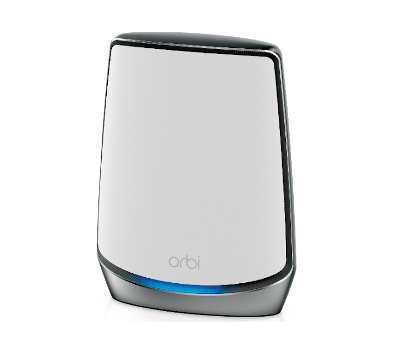
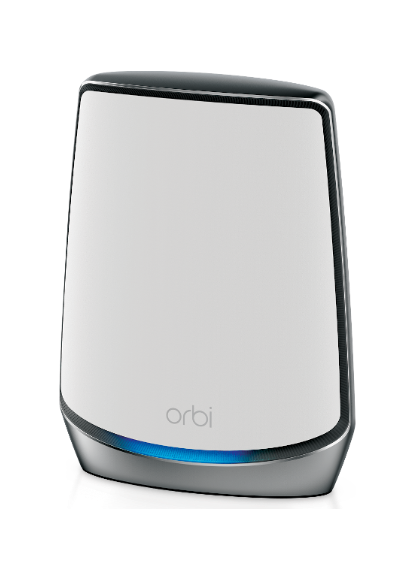


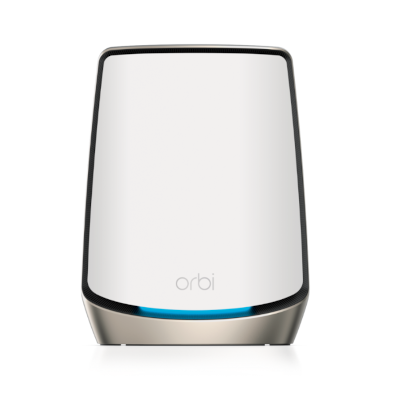
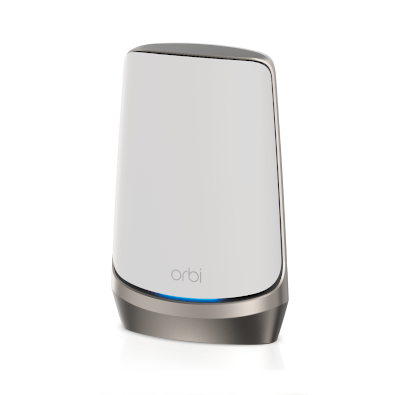


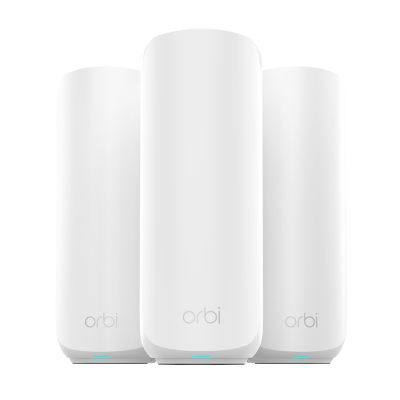

An authentication bypass vulnerability in NETGEAR Orbi devices allows users connected to the local network to access the router web interface as an admin.
Severity: MEDIUM
Acknowledgments: Fulaige
Recommendation
Devices with automatic updates enabled may already have this patch applied. If not, please check the firmware version and update it to the latest.
Fixed in:
CBR750 firmware V4.6.14.8 or later
NBR750 firmware V4.6.15.14 or later
RBE370 firmware v12.1.3.11 or later
RBE371 firmware v12.1.3.11 or later
RBE372 firmware v12.1.3.11 or later
RBE373 firmware v12.1.3.11 or later
RBE374 firmware v12.1.3.11 or later
RBE770 firmware v10.5.20.7 or later
RBE771 firmware v10.5.20.7 or later
RBE772 firmware v10.5.20.7 or later
RBE773 firmware v10.5.20.7 or later
RBE970 firmware v9.13.2.1 or later
RBE971 firmware v9.13.2.1 or later
RBR750 firmware v7.2.8.2 or later
RBR840 firmware v7.2.8.2 or later
RBR850 firmware v7.2.8.2 or later
RBR860 firmware v7.2.8.2 or later
RBS750 firmware v7.2.8.2 or later
RBS840 firmware v7.2.8.2 or later
RBS850 firmware v7.2.8.2 or later
RBS860 firmware v7.2.8.2 or later
RBRE950 firmware v7.2.8.2 or later
RBRE960 firmware v7.2.8.2 or later
RBSE950 firmware v7.2.8.2 or later
RBSE960 firmware v7.2.8.2 or later


An insufficient authentication vulnerability in NETGEAR WiFi range extenders allows a network adjacent attacker with WiFi authentication or a physical Ethernet port connection to bypass the authentication process and access the admin panel.
Severity: MEDIUM
Acknowledgments: Mad_Max
Recommendation
Manually check the firmware version and update it to the latest.
Fixed in:
EX2800 firmware V1.0.1.82 or later
EX3110 firmware V1.0.1.82 or later
EX5000 firmware V1.0.1.82 or later
EX6110 firmware V1.0.1.82 or later
A path traversal vulnerability in NETGEAR WiFi range extenders allows an attacker with LAN authentication to access the router's IP and review the contents of the dynamically generated webproc file, which records the username and password submitted to the router GUI.
Severity: MEDIUM
Acknowledgments: chiphazard
Recommendation
Manually check the firmware version and update it to the latest.
Fixed in:
EX2800 firmware V1.0.1.82 or later
EX3110 firmware V1.0.1.82 or later
EX5000 firmware V1.0.1.82 or later
EX6110 firmware V1.0.1.82 or later
Affected Products
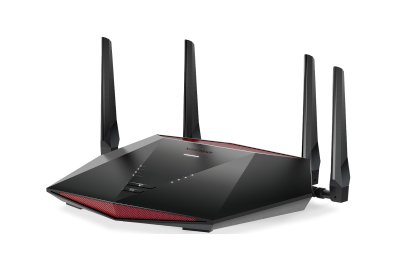
An insufficient input validation vulnerability in the NETGEAR XR1000v2 allows attackers connected to the router's LAN to execute OS command injections.
Severity: MEDIUM
Acknowledgments: o4ncL1
Recommendation
Devices with automatic updates enabled may already have this patch applied. If not, please check the firmware version and update it to the latest.
Fixed in:
Affected Products
An insufficient input validation vulnerability in NETGEAR Orbi devices' DHCPv6 functionality allows network adjacent attackers authenticated over WiFi or on LAN to execute OS command injections on the router. DHCPv6 is not enabled by default.
Severity: MEDIUM
Acknowledgments: Hyunseok Yun
Recommendation
Devices with automatic updates enabled may already have this patch applied. If not, please check the firmware version and update it to the latest.
Fixed in:
RBR750 firmware v7.2.8.5 or later
RBR840 firmware v7.2.8.5 or later
RBR850 firmware v7.2.8.5 or later
RBR860 firmware v7.2.8.5 or later
RBS750 firmware v7.2.8.5 or later
RBS840 firmware v7.2.8.5 or later
RBS850 firmware v7.2.8.5 or later
RBS860 firmware v7.2.8.5 or later
RBRE950 firmware v7.2.8.5 or later
RBRE960 firmware v7.2.8.5 or later
RBSE950 firmware v7.2.8.5 or later
RBSE960 firmware v7.2.8.5 or later
An insufficient input validation vulnerability in NETGEAR Orbi routers allows attackers connected to the router's LAN to execute OS command injections.
Severity: LOW
Acknowledgments: fxc233
Recommendation
Devices with automatic updates enabled may already have this patch applied. If not, please check the firmware version and update it to the latest.
Fixed in:
RBE971 firmware 9.10.0.2 or later
RBE970 firmware 9.10.0.2 or later
RBR750 firmware 7.2.8.5 or later
RBR850 firmware 7.2.8.5 or later
RBR860 firmware 7.2.8.5 or later
RBS750 firmware 7.2.8.5 or later
RBS850 firmware 7.2.8.5 or later
RBS860 firmware 7.2.8.5 or later
RBRE960 firmware 7.2.7.15 or later
RBSE960 firmware 7.2.7.15 or later
Disclaimer This document is provided on an "as is" basis and does not imply any kind of guarantee or warranty, including the warranties of merchantability or fitness for a particular use. Your use of the information in the document or materials linked to the document is at your own risk. NETGEAR reserves the right to change or update this document at any time. NETGEAR expects to update this document as new information becomes available.
The above-listed vulnerabilities remain if you do not complete all recommended steps. NETGEAR is not responsible for any consequences that could have been avoided by following the recommendations in this notification.