
NETGEAR's Product Security Team has assessed the following product vulnerabilities and provided guidance to address these vulnerabilities in the table below.
Since firmware updates include security improvements, bug fixes, and new features, we highly recommend enabling automatic updates on devices that support them. For older models, be sure to download and install the latest firmware as soon as possible, or follow any specific guidance given for your device.
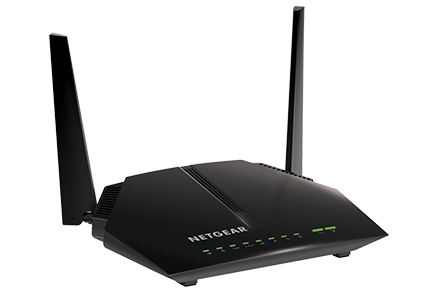
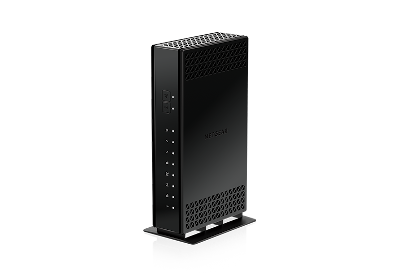
Denial of Service Vulnerability in NETGEAR C6220 and C6230 (DOCSIS® 3.0 Two-in-one Cable Modem + Wi-Fi Router) allows authenticated local WiFi users reboot the router.
Severity: MEDIUM
Acknowledgments: Quickdraw
Recommendation
NETGEAR strongly advises against allowing untrusted users or devices on your WiFi network. The NETGEAR C6220 has reached End-of-Support (EOS) and C6230 will reach EOS soon. Due to limited security impact (device reboots only), no fixes are planned.Affected Products
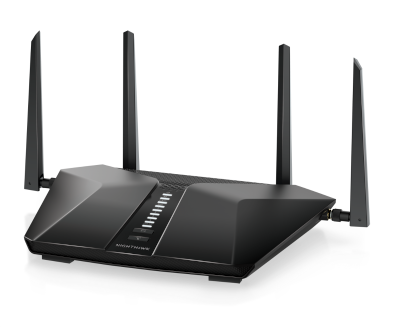
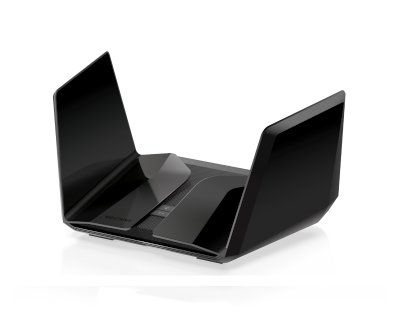
A vulnerability in the speedtest feature of affected NETGEAR Nighthawk routers, caused by improper input validation, can allow attackers on the router's WAN side, using attacker-in-the-middle techniques (MiTM) to manipulate DNS responses and execute commands when speedtests are run.
This issue affects RS700: through 1.0.7.82; RAX54Sv2 : before V1.1.6.36; RAX41v2: before V1.1.6.36; RAX50: before V1.2.14.114; RAXE500: before V1.2.14.114; RAX41: before V1.0.17.142; RAX43: before V1.0.17.142; RAX35v2: before V1.0.17.142; RAXE450: before V1.2.14.114; RAX43v2: before V1.1.6.36; RAX42: before V1.0.17.142; RAX45: before V1.0.17.142; RAX50v2: before V1.1.6.36; MR90: before V1.0.2.46; MS90: before V1.0.2.46; RAX42v2: before V1.1.6.36; RAX49S: before V1.1.6.36.
Severity: MEDIUM
Acknowledgments: molybdenum
Recommendation
Devices with automatic updates enabled may already have this patch applied. If not, please check the firmware version and update it to the latest.
Fixed in:
RS700 firmware V1.0.9.6 or later
RAX54Sv2/RAX45v2 firmware V1.1.6.36 or later
RAX41v2 firmware V1.1.6.36 or later
RAX50 firmware V1.2.14.114 or later
RAXE500 firmware V1.2.14.114 or later
RAX41 firmware V1.0.17.142 or later
RAX43 firmware V1.0.17.142 or later
RAX35v2 firmware V1.0.17.142 or later
RAXE450 firmware V1.0.17.142 or later
RAX43v2 firmware V1.1.6.36 or later
RAX42 firmware V1.0.17.142 or later
RAX45 firmware V1.0.17.142 or later
RAX50v2 firmware V1.1.6.36 or later
MR90 firmware V1.0.2.46 or later
MS90 firmware V1.0.2.46 or later
RAX42v2 firmware V1.1.6.36 or later
RAX49S firmware V1.1.6.36 or later
Affected Products
A vulnerability in NETGEAR Nighthawk R7000P routers lets an authenticated admin execute OS command injections due to improper input validation.
This issue affects R7000P: through 1.3.3.154.
Severity: LOW
Acknowledgments: SmallS
Recommendation
NETGEAR R7000P has reached End-of-Support phase, and no security updates are planned. NETGEAR strongly recommends that you retire this device and upgrade to a newer NETGEAR device for continued security support.Disclaimer This document is provided on an "as is" basis and does not imply any kind of guarantee or warranty, including the warranties of merchantability or fitness for a particular use. Your use of the information in the document or materials linked to the document is at your own risk. NETGEAR reserves the right to change or update this document at any time. NETGEAR expects to update this document as new information becomes available.
The above-listed vulnerabilities remain if you do not complete all recommended steps. NETGEAR is not responsible for any consequences that could have been avoided by following the recommendations in this notification.