

- Enable DHCP snooping globally.
(Netgear Switch) (Config)# ip dhcp snooping
- Enable DHCP snooping in a VLAN.
(Netgear Switch) (Config)# ip dhcp snooping vlan 1
- Configure the port through which the DHCP server is reached as trusted.
(Netgear Switch) (Config)# interface 1/0/1

	(Netgear Switch) (Interface 1/0/1)# ip dhcp snooping trust
- View the DHCP Snooping Binding table.
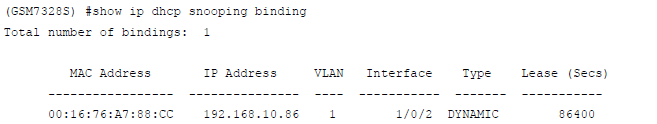
- Enable ARP inspection in VLAN 1.
(Netgear Switch) (Config)# ip arp inspection vlan 1
Now all ARP packets received on ports that are members of the VLAN are copied to the CPU for ARP inspection. If there are trusted ports, you can configure them as trusted in the next step. ARP packets received on trusted ports are not copied to the CPU.
- Configure port 1/0/1 as trusted.
(Netgear Switch) (Config)# interface 1/0/1

	(Netgear Switch) (Interface 1/0/1)# ip arp inspection trust
Now ARP packets from the DHCP client go through because there is a DHCP snooping entry; however ARP packets from the static client are dropped. It can be overcome by static configuration.
For more information, see the following support articles:
- How do I configure static mapping using CLI commands on my managed switch?
- What is Dynamic ARP inspection (DAI) and how does it work with my managed switch?
- How do I configure Dynamic ARP inspection (DAI) using the web interface on my managed switch?
This article applies to the following managed switches and their respective firmware:
- M5300 - firmware version 10.0.0.x
-
- M5300-28G (GSM7228S)
- M5300-5G (GSM7252S)
- M5300-28G3 (GSM7328Sv2h2)
- M5300-52G3 (GSM7352Sv2h2)
- M5300-28G_POE+ (GSM7228PSv1h2)
- M5300-52G-POE+ (GSM7252PSv1h2)
- M5300-28GF3 (GSM7328FSv2)
- M4100 - firmware version 10.0.1.x
-
- M4100-26G (GSM7224v2h2)
- M4100-50G (GSM7248v2h2)
- M4100-26G-POE (GSM7226Pv1h1)
- M4100-50G-POE+ (GSM7248Pv1h1)
- M4100-26G-POE (FSM7226Pv1h1)
- M4100-50-POE (FSM7250Pv1h1)
- M4100-D12G (GSM5212v1h1)
- M4100-D10-POE (FSM5210Pv1h1)
- M7100 - firmware version 10.0.1.x
-
- M7100-24X (XSM7224)
- XSM7224S - firmware version 9.0.1.x
Last Updated:07/07/2025
|
Article ID: 21809